
Managed Cyber Defense Service
TeamCloud Managed Security Services
CyberShield — managed XDR, SIEM, firewall security and vulnerability management.
Outsource your cybersecurity operations to a team that runs them every day. CyberShield combines continuous protection, monitoring, vulnerability discovery, response and reporting into one managed service — so you get security outcomes without building an in-house SOC.
Customer security challenges
Most organisations are exposed because security operations are fragmented and reactive
- 01 No SOC team Security incidents are handled by general IT without dedicated security operations.
- 02 Fragmented tools Endpoint, firewall, server logs and cloud logs are not correlated.
- 03 Unknown vulnerabilities Open ports, unmanaged assets and high-risk vulnerabilities are often invisible.
- 04 Late detection Many incidents are discovered only after ransomware, compromise or service disruption.
- 05 Audit pressure Customers, ISO and internal audits require evidence-based security reporting.
- 06 Limited response Alerts need validation, containment advice, remediation priority and tracking.
Cyber risks grow when tools, logs and response ownership are not connected.
Our managed cyber defense solution
A single service, not a stack of licences
We do not simply resell software. We deliver a managed consulting and operations service that continuously protects, detects, reports and helps remediate cybersecurity risks.
- Continuous Protection Endpoint, firewall and Security Heartbeat working as one enforcement layer.
- Continuous Monitoring SIEM log collection with alert correlation across systems.
- Continuous Improvement Vulnerability scanning with remediation tracking, reviewed every month.
-
TeamCloud
Security Ops -
Sophos
XDR -
Sophos
NGFW -
Security
Heartbeat -
Wazuh
SIEM -
Vulnerability
Scanner -
Monthly
Report
Core service modules
What is actually deployed, and what it does for you
A complete managed security stack covering endpoints, network, logs, vulnerabilities and response.
Anti-malware, EDR and ransomware protection.
Protects PCs and servers from modern threats.
IPS, web filtering, application control and VPN.
Secures the perimeter and enforces network policy.
Endpoint-to-firewall health signal.
Automatically isolates or restricts risky devices.
Centralised logs and correlation.
Detects abnormal activity across systems.
Network discovery and risk scoring.
Finds exposed services, weak assets and patch gaps.
Monthly report and incident support.
Turns technical alerts into actionable business risk.
Endpoint · Firewall · Heartbeat · SIEM · Vulnerability · Reporting & Response
Ten critical cybersecurity capabilities
The controls your auditors and customers ask about
All ten are included within the managed service scope.
- Endpoint Protection
- Ransomware Protection
- Firewall Protection
- Intrusion Prevention
- Log Monitoring
- File Integrity Monitoring
- Vulnerability Assessment
- Cloud / Server Monitoring
- Compliance Reporting
- Incident Alert & Response
Reference service architecture
From your environment to managed operations, alerts and remediation
Customer environment
- EndpointsPC / laptop
- ServersWindows / Linux
- CloudVM / workload
- NetworkFirewall / switch / NAS
Security platforms
- Sophos XDREndpoint protection & investigation
- Sophos NGFWIPS, web, app control & gateway
- Wazuh SIEMLogs, FIM, compliance & correlation
- VA ScannerNetwork discovery & vulnerability scan
TeamCloud SOC
- Alert triageValidate & prioritise
- Incident supportContainment advice
- Monthly reviewRisk & action plan
Business outcomes
- Reduced riskLower ransomware and intrusion exposure
- Audit readyEvidence-based security reporting
- Clear actionsRemediation priority list
- No in-house SOCSecurity operations outsourced
Service delivery process
A repeatable lifecycle, from baseline assessment to continuous improvement
- Initial security assessmentAsset review, IP ranges and risk baseline.
- Deployment & integrationAgents, firewall policies, logs and scanner setup.
- Baseline vulnerability scanFirst view of exposed services and patch gaps.
- Continuous monitoringEndpoint, server, firewall and cloud log monitoring.
- Alert analysisValidate alerts and prioritise incidents.
- Monthly security reportExecutive summary and technical remediation list.
- Remediation reviewTrack fixes and tune security rules.
- Quarterly improvementSecurity roadmap and posture improvement.
What customers receive
Clear visibility, practical guidance, measurable risk reduction
From scattered alerts to clearer security decisions.
Who this is for
Built for organisations that need security outcomes without a SOC team
Why TeamCloud
A security service built on real infrastructure experience
We are positioned to deliver this because we understand the full IT stack — from endpoints and servers to cloud infrastructure, firewalls, backup and disaster recovery.
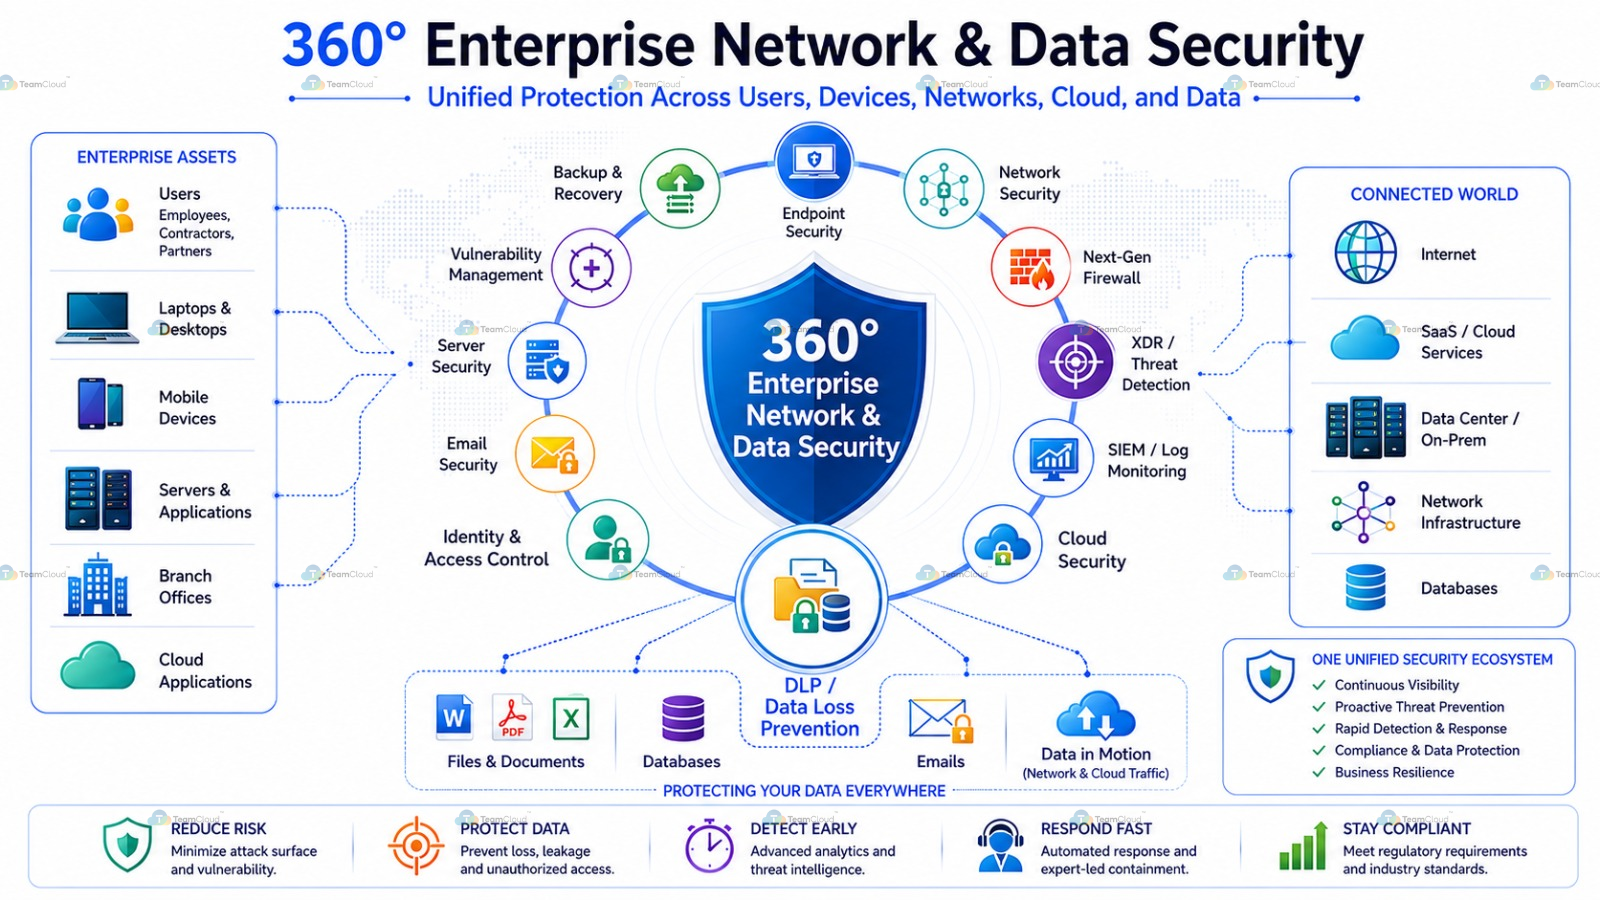
& Data Security
At a glance
The full picture
Unified protection across users, devices, networks, cloud and data.
Questions
Frequently asked questions
Is this just software resale?
What technology does the service run on?
Do we need our own security team to run this?
What do we actually get each month?
How does deployment work?
Which package should we choose?
Will this help with our ISO audit or customer security questionnaires?
How is it priced?
Start with a security assessment
Discover your risks before choosing a package
Find your current risks, vulnerabilities and security gaps first — then decide the right managed security package.
- Step 1Baseline security review
- Step 2Deploy managed monitoring
- Step 3Report, respond & improve
TeamCloud CyberShield Managed Security Service · Managed XDR | SIEM | Firewall Security | Vulnerability Management | Incident Support


